Skip to content
Caudilysis · A Caudify product

Static code analysis for security, engineering & compliance.

Caudilysis is a static code analysis tool that scans your codebase once and reports security vulnerabilities, engineering quality and compliance evidence together. One scan shows you what an attacker, an architect and an auditor would each find in your code, with an AI advisor that explains every score in plain English.
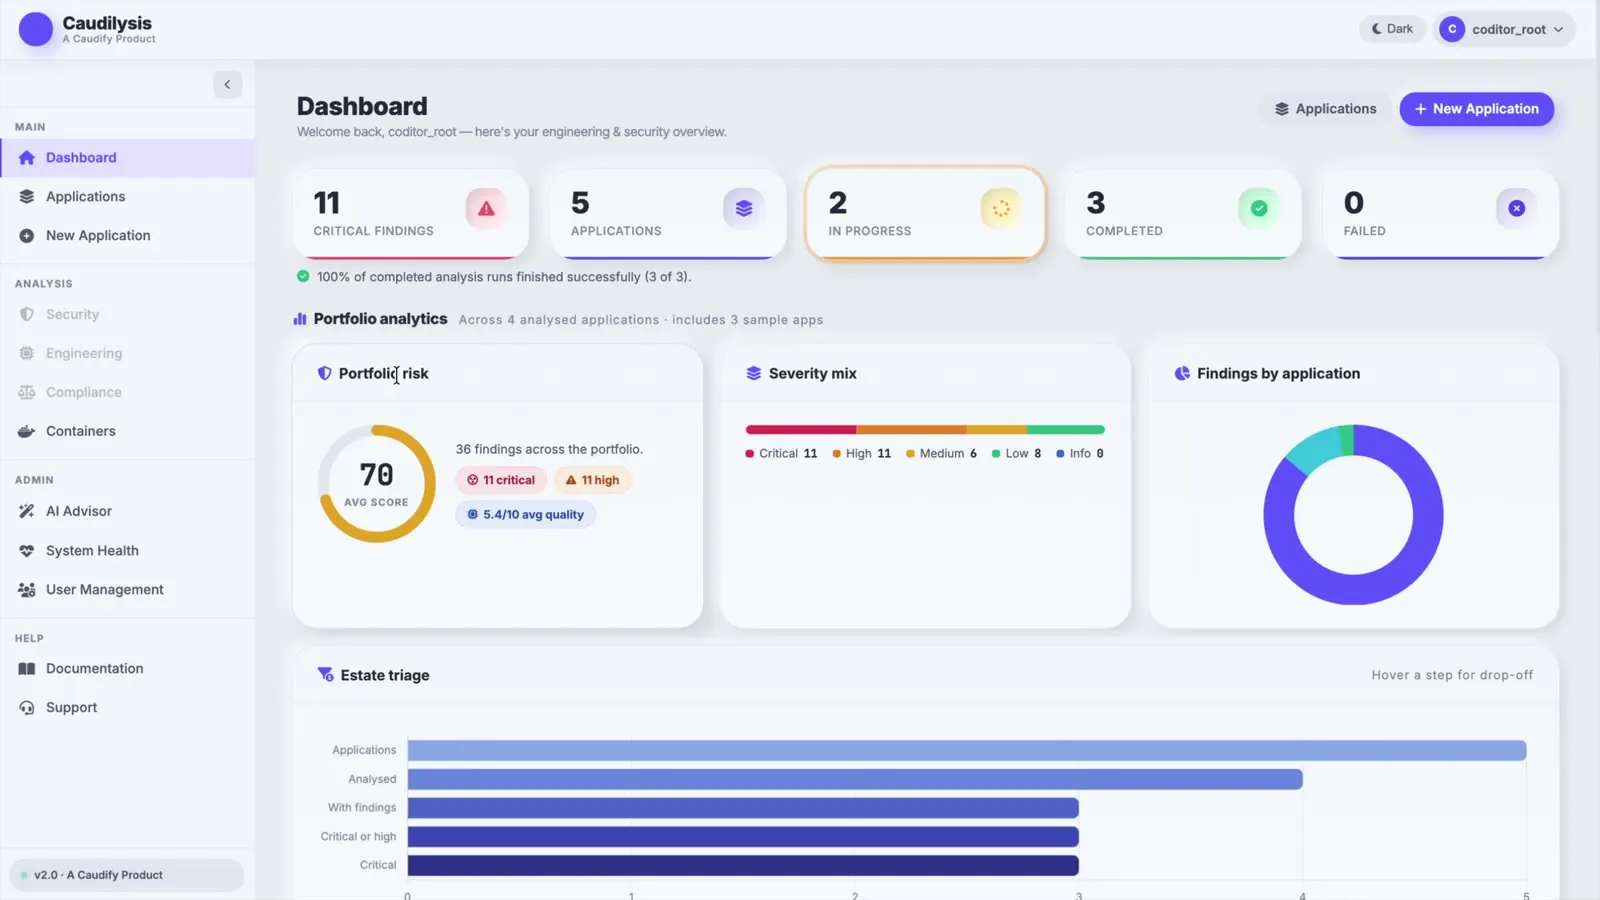
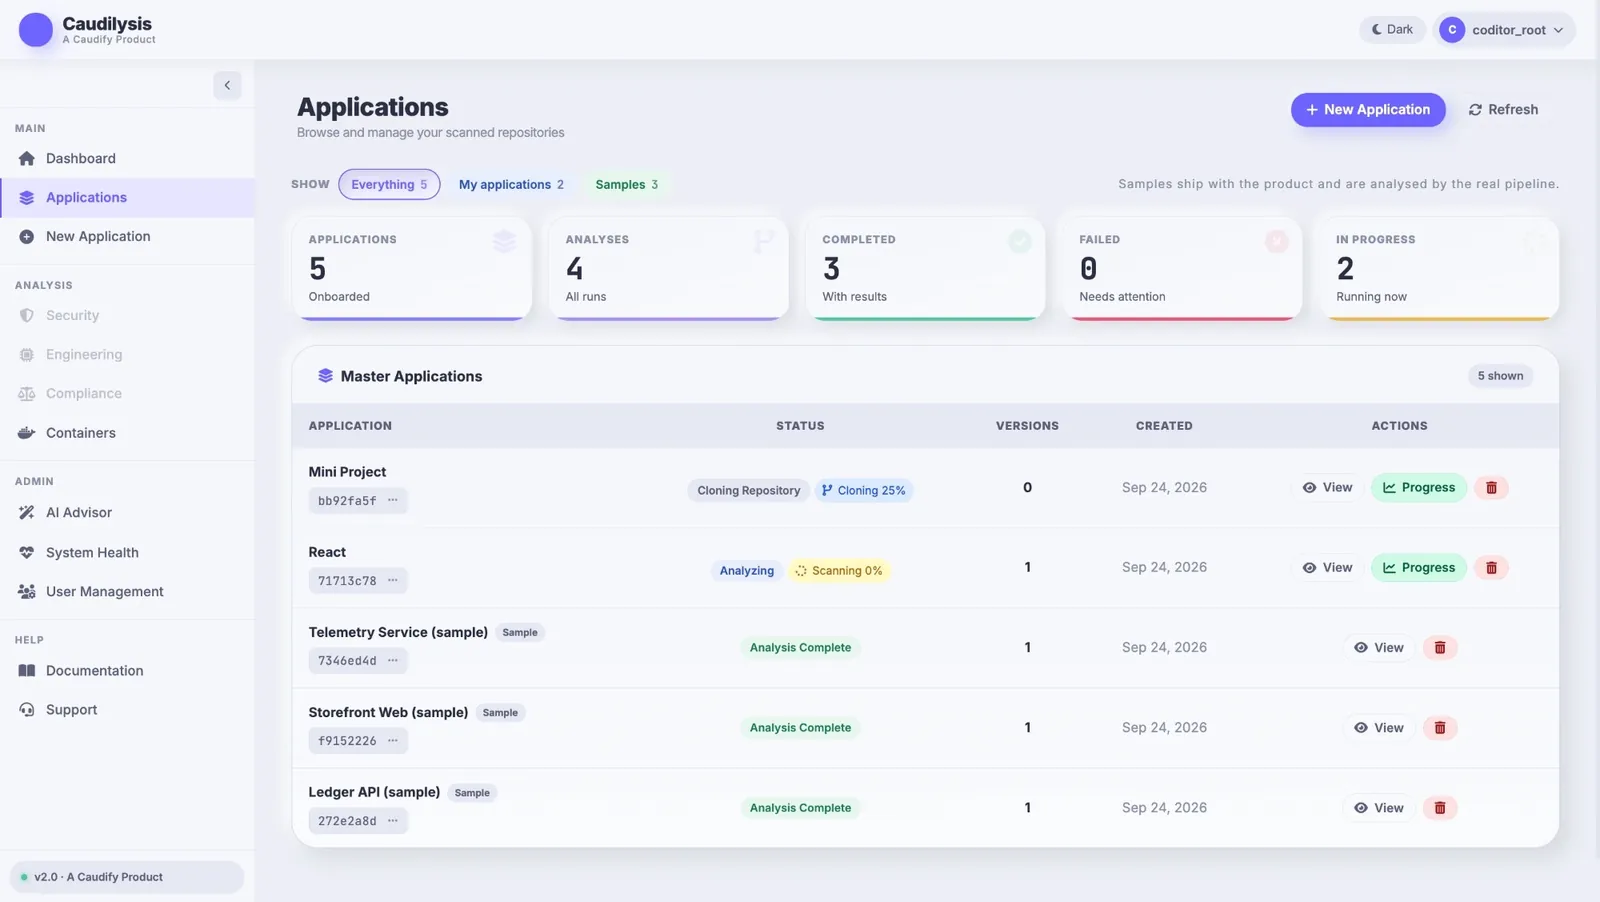
Caudilysis product walkthrough showing the dashboard, applications, analysis results, security, engineering and compliance analytics.
100SecurityStrong posture
3.8Engineering · /10Needs improvement
68Compliance3 of 14 controls passing

Scores from a sample scan of a React application.

One scan, three lenses

Security, engineering and compliance from a single scan.

Catch vulnerabilities before they ship.

Static analysis for real world security. Injection risks, unsafe dynamic code, insecure transport, hardcoded secrets and vulnerable dependencies are ranked by severity, so teams fix what carries the most risk first.
  • SAST across common vulnerability classes
  • Secret and credential detection
  • Dependency and supply chain checks
  • Severity ranked, per file findings
On the screen
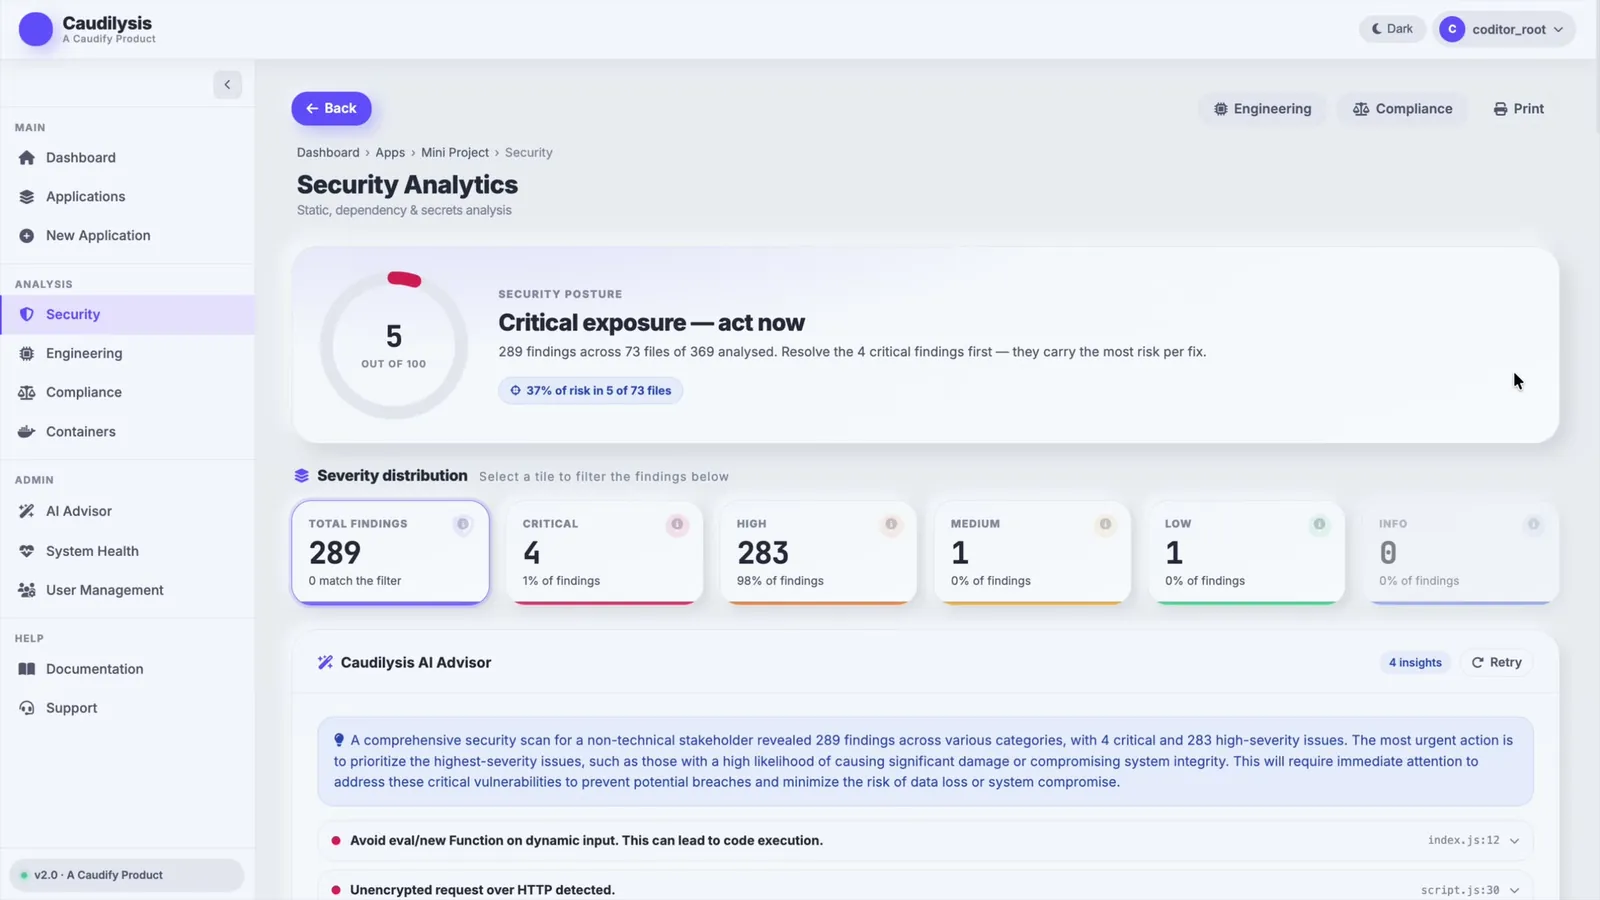
  1. 1Posture score out of 100
  2. 2Severity distribution with filterable findings
  3. 3AI advisor’s summary and top actions
Caudilysis Security Analytics showing a posture score of 5 out of 100, 289 findings by severity and the AI advisor summary.
Caudilysis AI Advisor

Findings, explained the way a senior engineer would.

Scores tell you something is wrong. The advisor tells you what, why it matters, and what to do first, in language a stakeholder can read.
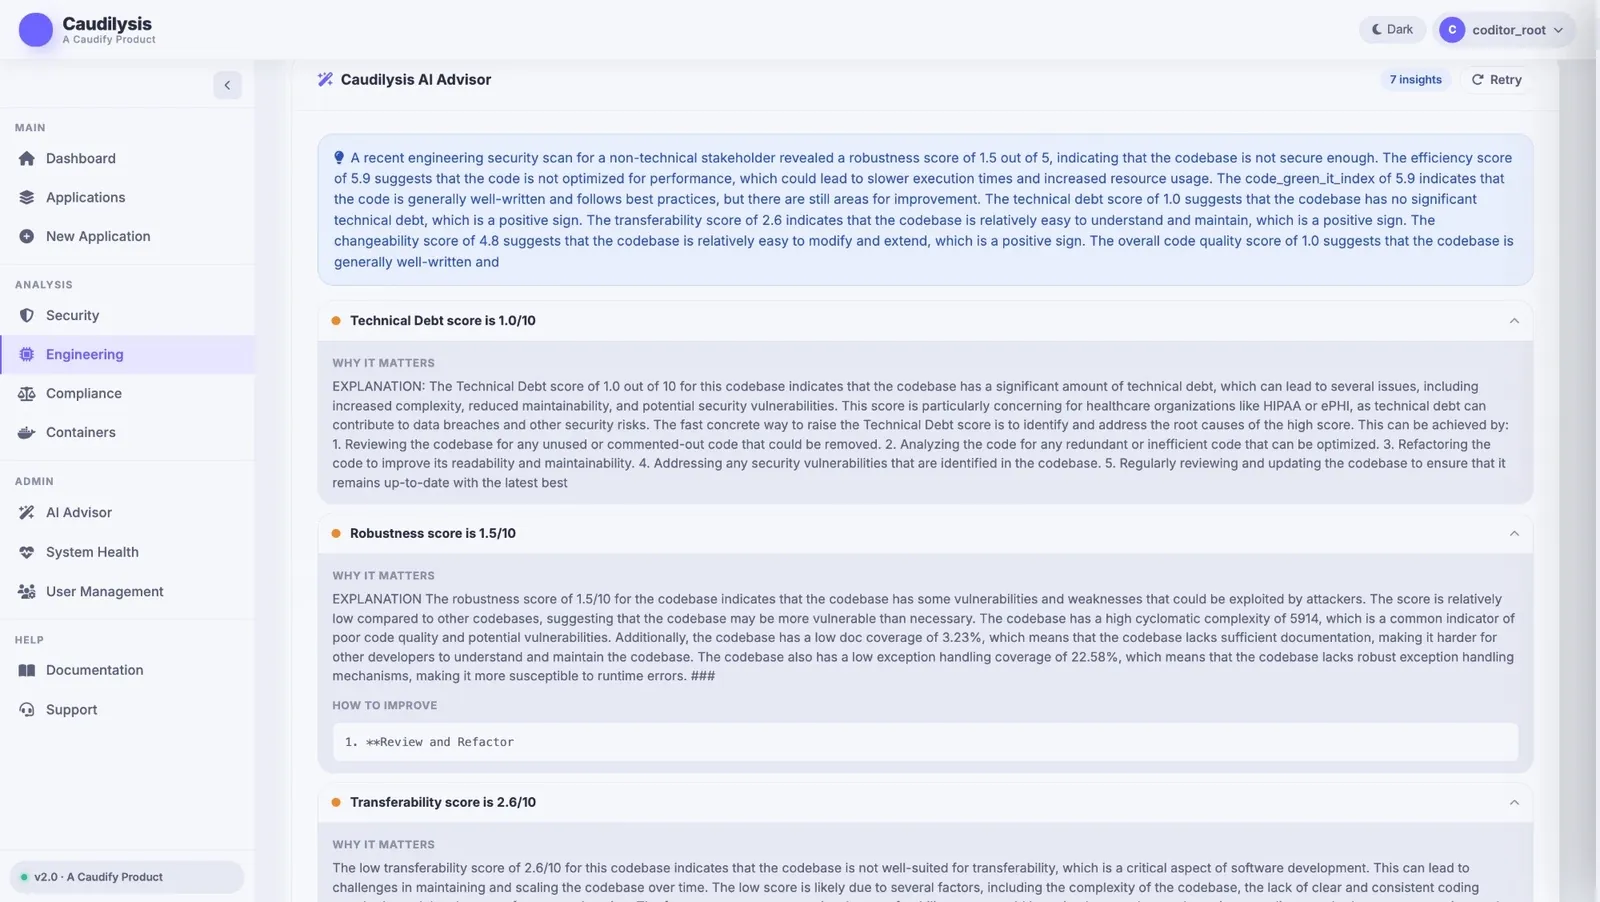
  1. A plain English summaryThe whole analysis in a paragraph, written for nontechnical stakeholders.
  2. Why it mattersEvery insight tied to its score and to the real risk it carries.
  3. How to improveConcrete next steps, ordered so the fastest wins come first.
The Caudilysis AI Advisor panel with a plain English summary and expandable insights on technical debt, robustness and transferability scores.7 insights · generated per analysis
Codebase intelligence

Know where the risk lives, down to the file.

Every view below is a real Caudilysis screen. Select one to see it full size.

Who it's for

For teams that treat security, quality and compliance as product requirements.

Caudilysis is built for organisations that already know what a vulnerability, a brittle module or a failed audit costs, and want all three measured on every release of their software, products and web applications.

  • Engineering leaders & CTOs

    Track code quality, technical debt and maintainability across every application, and set quality gates the whole team ships against.

  • Security & AppSec teams

    Find vulnerabilities, leaked secrets and risky dependencies before release, mapped to OWASP Top 10 and CWE Top 25.

  • Compliance & audit owners

    Turn every scan into evidence for OWASP ASVS and ISO/IEC 27001:2022 instead of collecting it by hand before each audit.

  • Enterprises & regulated teams

    Run Caudilysis as SaaS, or on a private, dedicated deployment when your code needs a high security environment.

From repo to report

Four steps. No setup marathon.

The Onboard step in Caudilysis
Step 1 of 4

Onboard

Add a repository, or start from a bundled sample. Every application keeps its versions and its scan history.
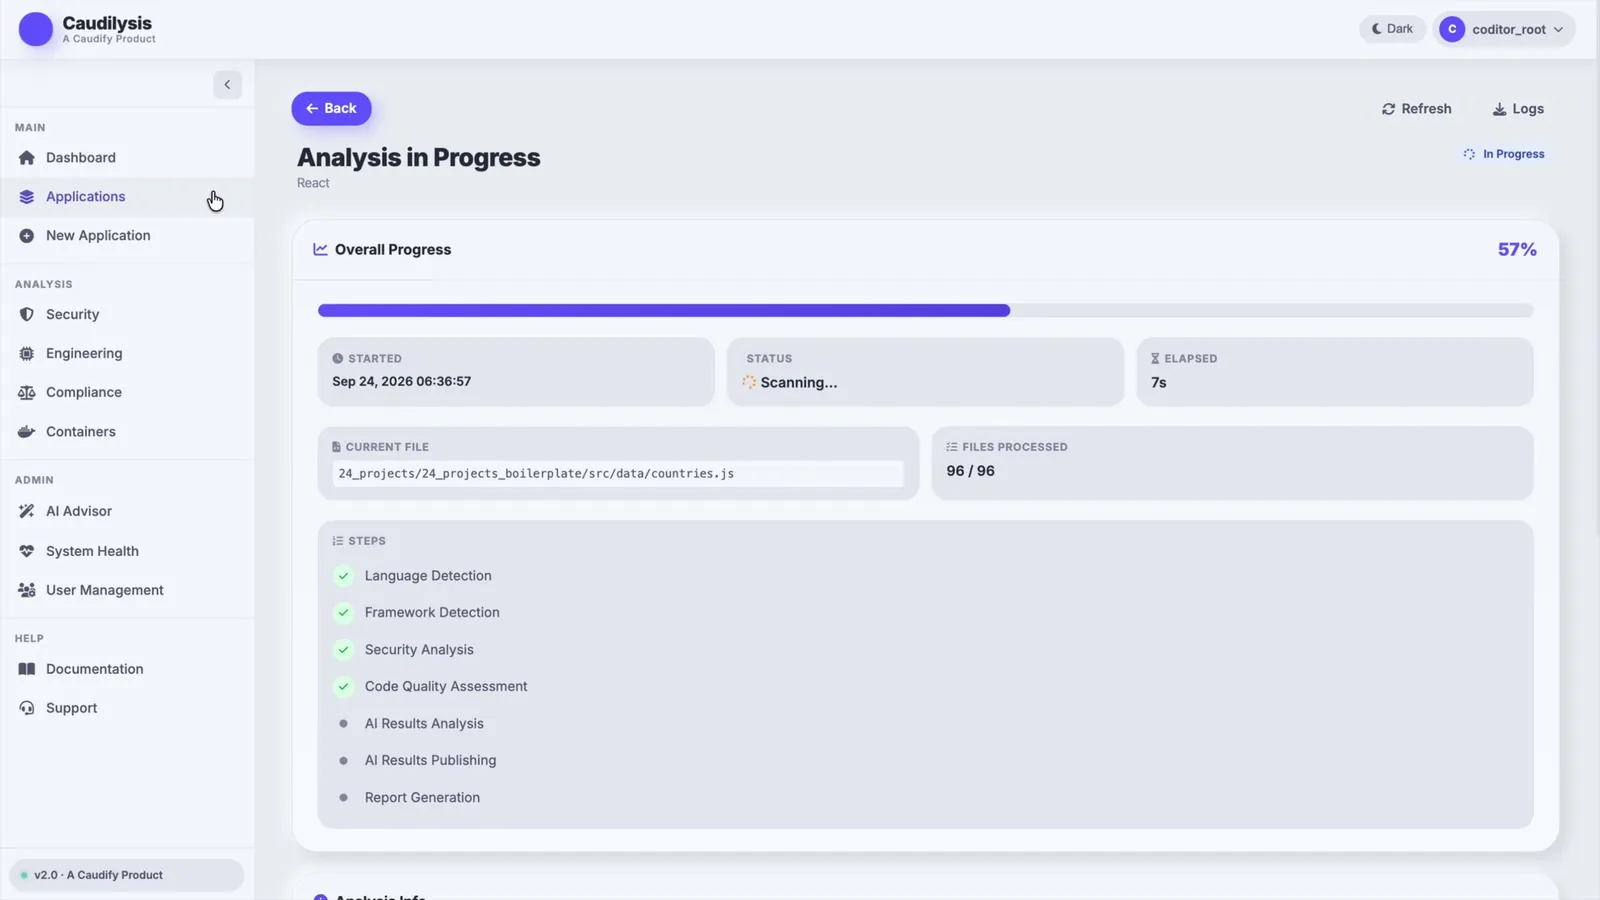
The Analyze step in Caudilysis
Step 2 of 4

Analyze

Language and framework detection, security analysis and code quality assessment, then AI analysis and the report, tracked step by step.
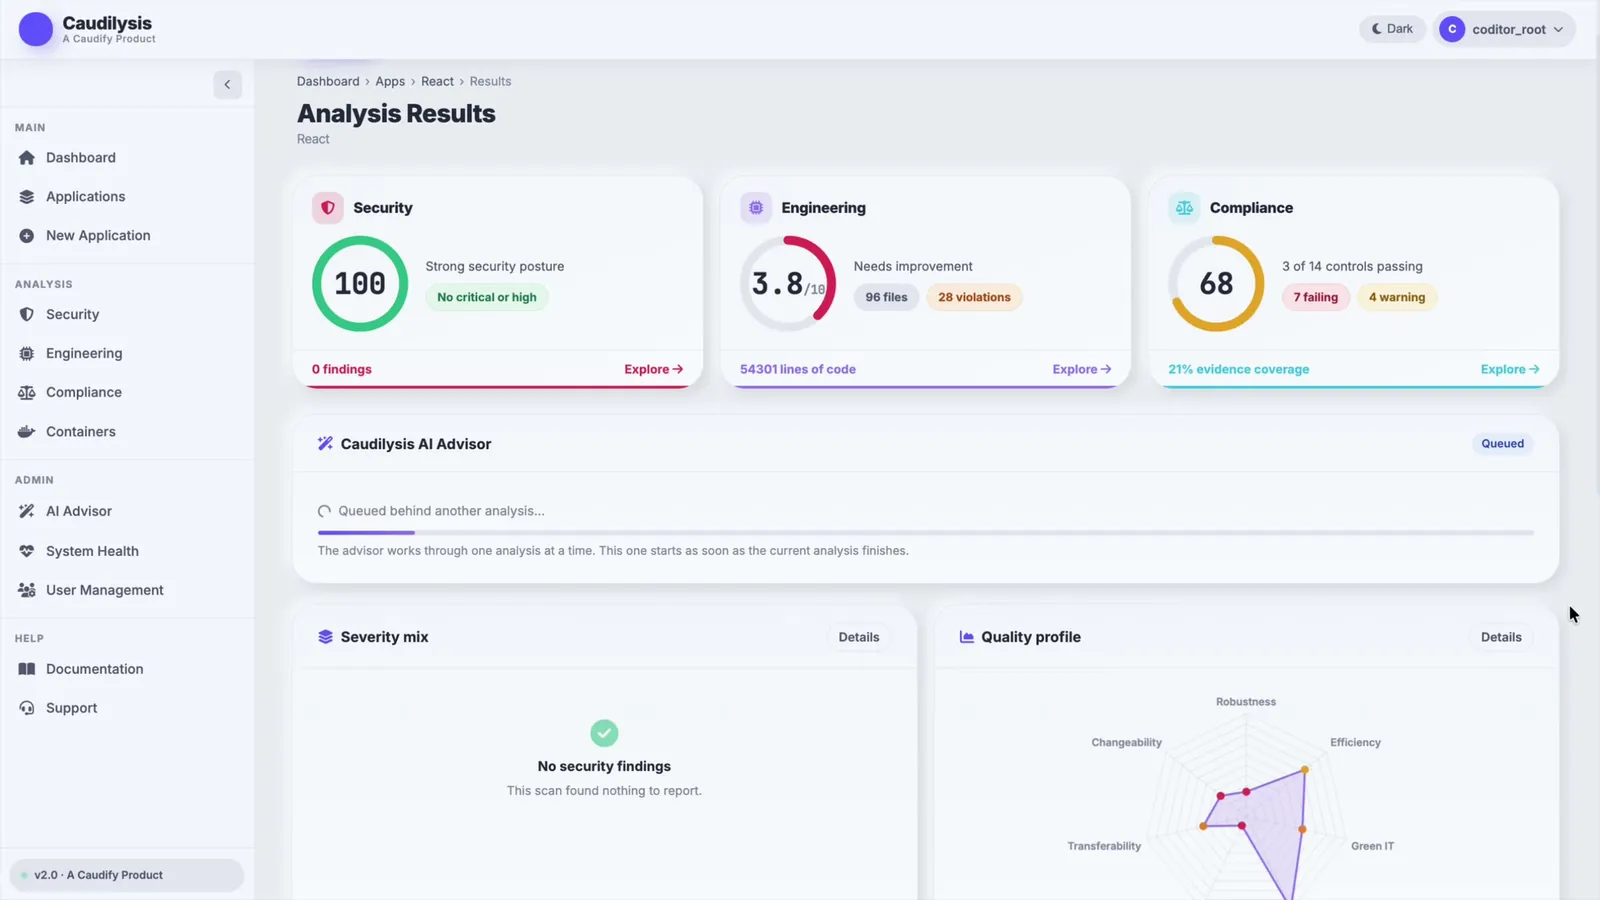
The Review step in Caudilysis
Step 3 of 4

Review

One results page with a score for each lens, the severity mix, the quality profile and the AI advisor’s summary.
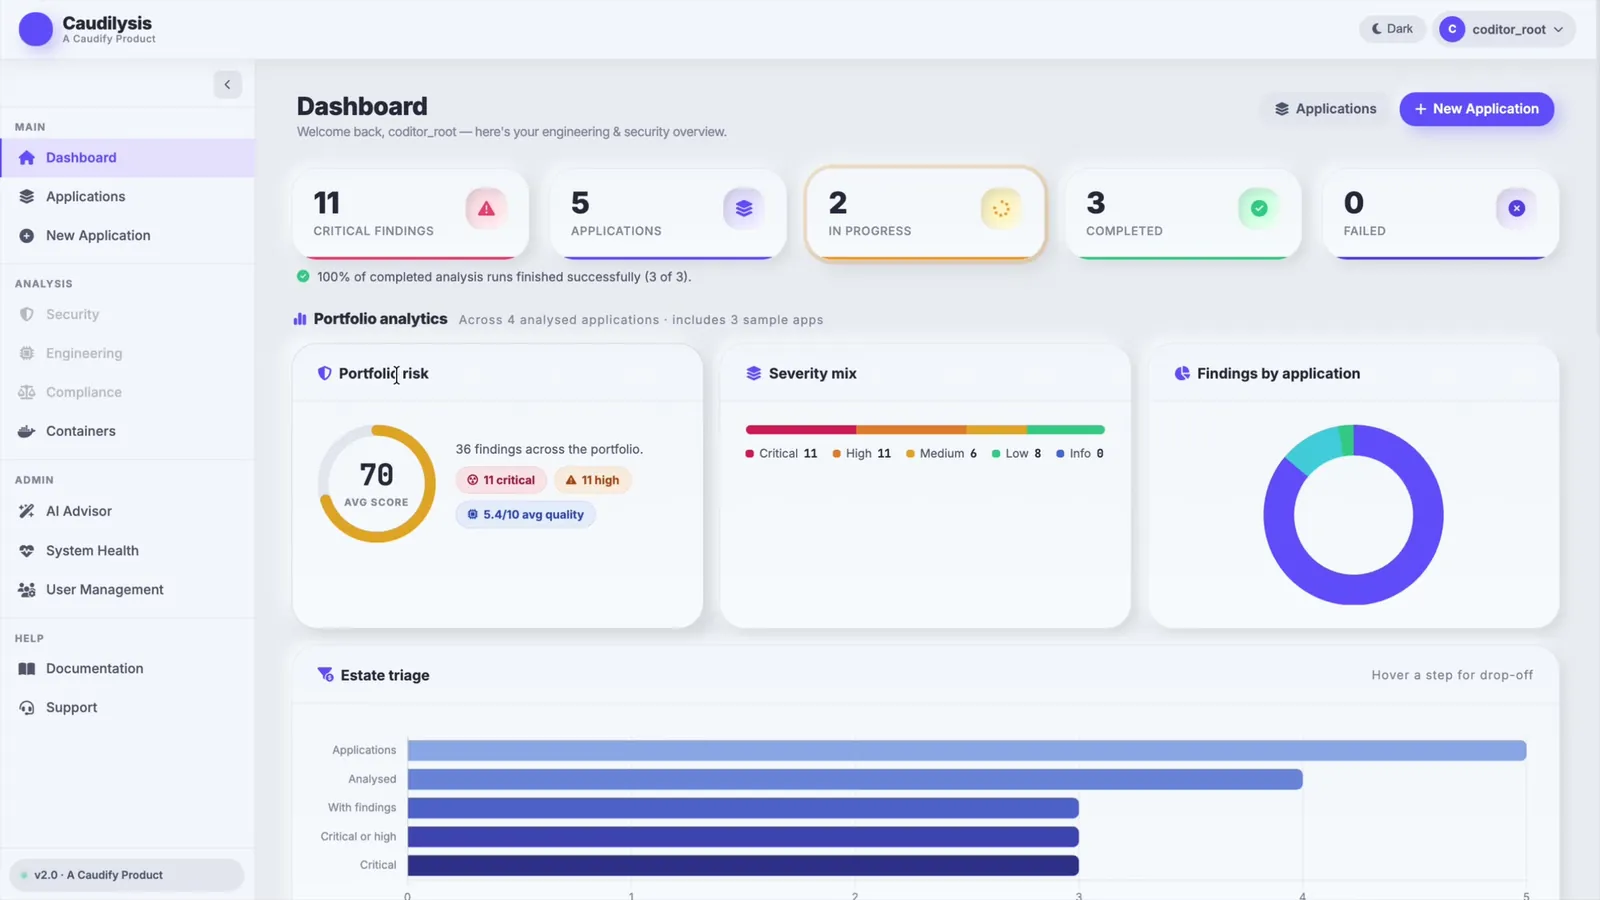
The Monitor step in Caudilysis
Step 4 of 4

Monitor

Track every application from one dashboard, with portfolio risk, severity mix and triage across the whole estate.

Pricing

One price per organisation, not per developer.

Security, engineering quality and compliance in one plan, from a growing team to a private, dedicated deployment. Every plan includes onboarding by our team.

  • Team

    Small to mid size engineering teams

    $1,190per month, billed yearlyor $1,490 billed monthly

    Users
    Up to 10
    Applications
    10
    • Security, engineering & compliance scans
    • OWASP Top 10 & CWE Top 25 mapping
    • AI advisor, pull request & CI/CD scanning
    • JSON & PDF reports, onboarding included
  • Enterprise

    Large organisations

    $7,490per month, billed yearly

    Users
    Up to 100
    Applications
    Unlimited
    • Everything in Business
    • Enterprise SLA
    • Onboarding & training for your teams
    • Yearly billing only
  • Private / Dedicated

    High security environments

    Let's talkcustom contract

    Users
    Unlimited
    Applications
    Unlimited
    • Everything in Enterprise
    • Private, dedicated deployment
    • Custom security & support terms
    • One time setup fee

Prices in USD, excluding taxes. Yearly plans are billed upfront; monthly plans can be cancelled any time. Need more users or applications? We'll size a plan with you.

Roadmap

Where Caudilysis goes next.

Today Caudilysis is static code analysis: one scan of your codebase for security, engineering quality and compliance, explained by the AI advisor. Next, it moves to where code is written and reviewed.

  • Planned

    Git review on pull requests

    Caudilysis findings and AI advisor explanations posted as review comments on the pull request itself, in the Git tools your team already uses, so issues are caught and explained before they merge.

  • Planned

    VS Code extension

    Findings and plain English explanations inside the editor while code is being written, including code from AI assistants, long before it reaches a pull request.

Planned features are not available yet and are not part of current plans. Want one sooner? Tell us which matters most to your team.

Questions

What teams ask before they scan.

What does Caudilysis analyse?
Your source code, in one scan, through three lenses. Security (vulnerabilities, secrets, dependencies), engineering quality (robustness, efficiency, changeability, technical debt and more) and compliance (controls mapped to recognised frameworks with evidence).
Which compliance frameworks does it map to?
Analyses produce evidence for OWASP Top 10 (2021 and 2025), CWE Top 25, OWASP ASVS and ISO/IEC 27001:2022. Frameworks such as SOC 2, PCI DSS, HIPAA and GDPR appear automatically once the analyser reports control data for them.
Is Caudilysis an AI code review tool?
Today Caudilysis is static code analysis with an AI advisor: it scans your codebase and explains every finding in plain English. Git review, with Caudilysis findings and explanations posted as comments on your pull requests, and a VS Code extension are on the roadmap. Until they ship, teams use Caudilysis reports alongside their normal code review.
Does Caudilysis work on AI-generated code?
Yes. Static analysis reads source code whoever or whatever wrote it, so Caudilysis is a useful check on code produced by AI coding assistants, which often works but misses input validation, authorisation or safe defaults.
What is the Caudilysis AI Advisor?
An assistant that reads each analysis and explains it in plain English. You get a summary for nontechnical stakeholders, then per issue insights covering why it matters and how to improve, so teams know what to fix first.
Does it fit into our CI/CD pipeline?
Yes. Caudilysis is designed to run where your code lives, on pull requests and in CI, with quality gates you control, and results you can export as JSON or PDF.
How is Caudilysis delivered?
As SaaS hosted by Caudify, or as a private, dedicated deployment for high security environments. Our team handles the deployment, so you aren't left configuring scanners yourself.
How much does Caudilysis cost?
Plans are priced per organisation, not per developer. Team is $1,190 a month billed yearly ($1,490 monthly) for up to 10 users, Business is $2,990 ($3,690 monthly) for up to 30, and Enterprise is $7,490 a month billed yearly for up to 100 users and unlimited applications. Private, dedicated deployments are quoted.
Get started

Put Caudilysis on your codebase.

Tell us your stack and what you need to cover, whether that's security, engineering standards, compliance or all three, and we'll set you up with a first scan.

See our other product, Caudify CRMS